
Blog
Our latest news.
Stay up-to-date with news and blog posts from ASMGi on how to bridge the gap to apply technology to solve business problems.
ASMGi Posts

Navigating AI-Era Cyber Risk: Security, Compliance & Insurance

IT Chaos Solved: Intune + Autopilot in Action

Fail SOC 2 Once – Pay Forever

Essential AI Strategies to Strengthen Third Party Risk Management

Cyber Insurance: Making the Most of Your Policy

Preventing Breaches: The Power of Security Awareness Training

Webinar: Resiliency in the Face of Ransomware

Zero Trust: A Paradigm Shift in Cybersecurity

Unveiling Deception: How to Spot Scams Before They Spot You

Ransomware: Strategies for Safeguarding Your Digital Assets

Unraveling the Power of AI in Cybersecurity: Safeguarding the Digital Realm

Fortifying Cybersecurity Defenses

Optimizing Healthcare Cybersecurity Cost and Staffing: Balancing Resources and Risk in Healthcare

Leading Cybersecurity Companies GS Lab | GAVS and ASMGi Announce Strategic Partnership to Enhance Global Cyber Defense

Understanding the Importance of Third-Party Risk Management in Healthcare

Embracing Smart Manufacturing: Unveiling IoT Trends, Challenges, and Cybersecurity in the Era of Industry 4.0

Cybersecurity Update – Terin D. Williams – DHS – CISA

Real Life Cyber Attacks - Dec 1 Event

The age of IoT and AI is quickly advancing, demanding more compute power and lower latency at the edge to ensure quick response and great performance.

xIoT Device Risk: Turning the Industry Inside-Out

Cyber Insurance: Digital Risk Mitigation Plan From Financial Loss

AI In Healthcare
Cybersecurity News from Around the Web
New ‘Deep Learning Attack’ Deciphers Laptop Keystrokes with 95% Accuracy
A group of academics has devised a "deep learning-based acoustic side-channel attack" that can be used to classify laptop keystrokes that are recorded using a nearby phone with 95% accuracy. "When trained on keystrokes recorded using the video conferencing software...
New SkidMap Redis Malware Variant Targeting Vulnerable Redis Servers
Vulnerable Redis services have been targeted by a "new, improved, dangerous" variant of a malware called SkidMap that's engineered to target a wide range of Linux distributions. "The malicious nature of this malware is to adapt to the system on which it is executed,"...
How an 8-character password could be cracked in just a few minutes
Advances in graphics processing technology and AI have slashed the time needed to crack a password using brute force techniques, says Hive Systems.
FBI Alert: Crypto Scammers are Masquerading as NFT Developers
The U.S. Federal Bureau of Investigation (FBI) is warning about cyber crooks masquerading as legitimate non-fungible token (NFT) developers to steal cryptocurrency and other digital assets from unsuspecting users. In these fraudulent schemes, criminals either obtain...
MDR: Empowering Organizations with Enhanced Security
Managed Detection and Response (MDR) has emerged as a crucial solution for organizations looking to bolster their security measures. MDR allows businesses to outsource the management of Endpoint Detection and Response (EDR) products deployed across their network...
Reptile Rootkit: Advanced Linux Malware Targeting South Korean Systems
Threat actors are using an open-source rootkit called Reptile to target Linux systems in South Korea. "Unlike other rootkit malware that typically only provide concealment capabilities, Reptile goes a step further by offering a reverse shell, allowing threat actors to...
Microsoft Addresses Critical Power Platform Flaw After Delays and Criticism
Microsoft on Friday disclosed that it has addressed a critical security flaw impacting Power Platform, but not before it came under criticism for its failure to swiftly act on it. "The vulnerability could lead to unauthorized access to Custom Code functions used for...
Researchers Uncover New High-Severity Vulnerability in PaperCut Software
Cybersecurity researchers have discovered a new high-severity security flaw in PaperCut print management software for Windows that could result in remote code execution under specific circumstances. Tracked as CVE-2023-39143 (CVSS score: 8.4), the flaw impacts...
UK’s NCSC Publishes New Shadow IT Guidance
Discover the new shadow IT guidance published by the U.K.'s NCSC. Use this guide to better identify and reduce the levels of shadow IT within your organization.
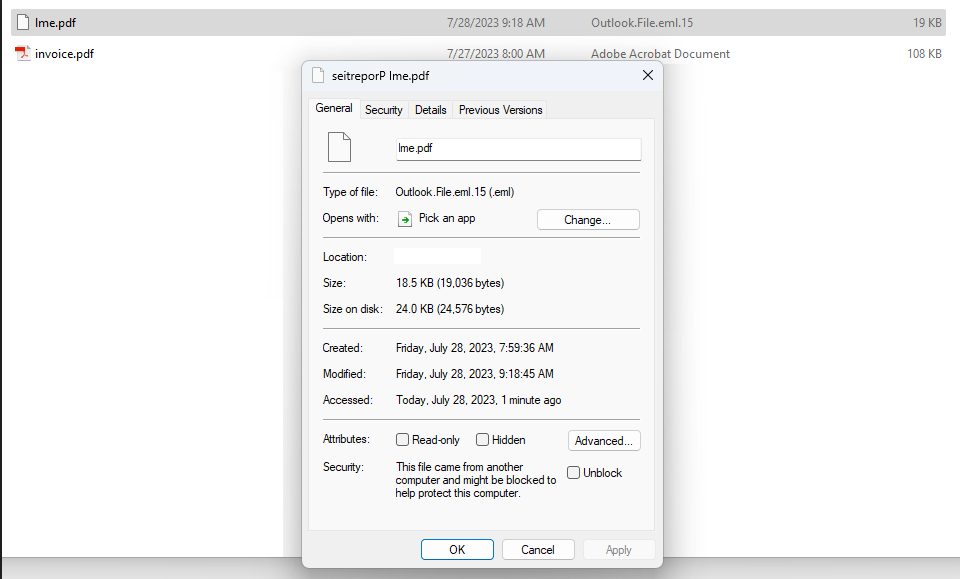
Teach a Man to Phish and He’s Set for Life
One frustrating aspect of email phishing is the frequency with which scammers fall back on tried-and-true methods that really have no business working these days. Like attaching a phishing email to a traditional, clean email message, or leveraging link redirects on...