
Blog
Our latest news.
Stay up-to-date with news and blog posts from ASMGi on how to bridge the gap to apply technology to solve business problems.
ASMGi Posts
Navigating AI-Era Cyber Risk: Security, Compliance & Insurance
IT Chaos Solved: Intune + Autopilot in Action
Fail SOC 2 Once – Pay Forever
Essential AI Strategies to Strengthen Third Party Risk Management
Cyber Insurance: Making the Most of Your Policy
Preventing Breaches: The Power of Security Awareness Training
Webinar: Resiliency in the Face of Ransomware
Zero Trust: A Paradigm Shift in Cybersecurity
Unveiling Deception: How to Spot Scams Before They Spot You
Ransomware: Strategies for Safeguarding Your Digital Assets
Unraveling the Power of AI in Cybersecurity: Safeguarding the Digital Realm
Fortifying Cybersecurity Defenses
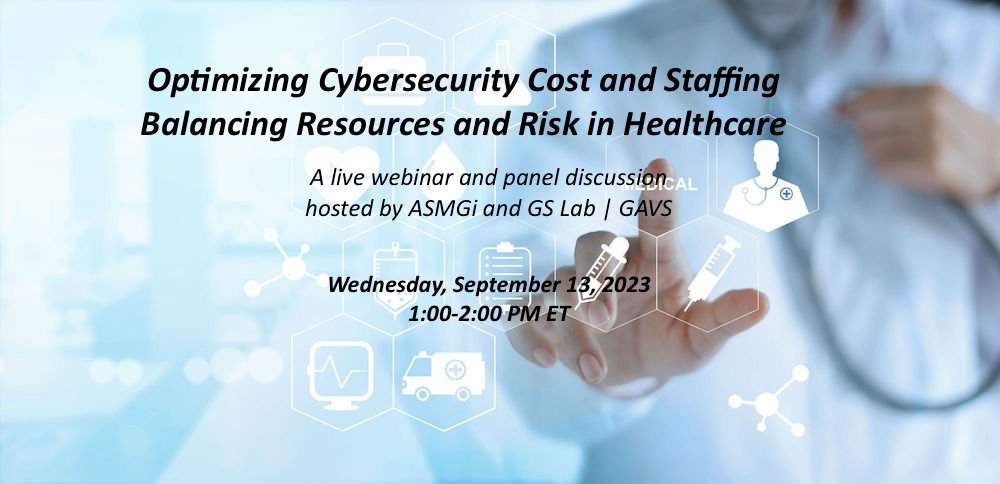
Optimizing Healthcare Cybersecurity Cost and Staffing: Balancing Resources and Risk in Healthcare
Leading Cybersecurity Companies GS Lab | GAVS and ASMGi Announce Strategic Partnership to Enhance Global Cyber Defense
Understanding the Importance of Third-Party Risk Management in Healthcare
Embracing Smart Manufacturing: Unveiling IoT Trends, Challenges, and Cybersecurity in the Era of Industry 4.0
Cybersecurity Update – Terin D. Williams – DHS – CISA
Real Life Cyber Attacks - Dec 1 Event
The age of IoT and AI is quickly advancing, demanding more compute power and lower latency at the edge to ensure quick response and great performance.
xIoT Device Risk: Turning the Industry Inside-Out
Cyber Insurance: Digital Risk Mitigation Plan From Financial Loss
AI In Healthcare
Cybersecurity News from Around the Web
CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day
Google says a Pixel modem zero-day was under targeted exploitation. CISA has added CVE-2026-58704 to KEV as users are urged to patch. The post CISA Gives Agencies 3 Days to Patch Exploited Pixel Zero-Day appeared first on TechRepublic.
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point's Security Management and Log Servers could allow an attacker without login credentials to run code as root on those servers over the network. The Security Management Server is the system that controls firewall policy and...
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools, exposed services, old bugs, weak logins, and software sold like a monthly subscription. Some attacks use new tricks. Others...
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere else on the host, Docker warns in a security announcement on September 15. The escape runs with the rights of...
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. "HEAVYGRAM offers builtin commands supporting remote command execution, system,...
Iran-Linked Handala Hack Tied to HEAVYGRAM Telegram Backdoor That Can Steal Passwords
The Iran-linked "hacktivist" persona known as Handala Hack has been attributed to a Telegram-based surveillance backdoor called HEAVYGRAM and a Delphi-based utility known as CRUDEEXCLUDE. "HEAVYGRAM offers builtin commands supporting remote command execution, system,...
Critical Unbound DNSSEC Validator Flaw Could Allow RCE via a Malicious DNS Zone
Every release of the Unbound DNS resolver before 1.26.1 has a critical heap overflow in its DNSSEC validator, maintainer NLnet Labs said in an advisory on Wednesday. An attacker who controls a malicious zone and queries a vulnerable resolver can trigger it, enabling...
Can You Prove a New CVE Is Exploitable Before Attackers Do? Learn How in This Webinar
A new CVE drops. Your scanner finds it. The severity score looks ugly. But that still does not answer the question that matters: Can it actually be exploited in your environment? Mythos-class AI is compressing the time between disclosure and working exploitation,...
CISO’s Expert Guide to Agentic Pentesting for Websites
Attackers now weaponize new vulnerabilities in about five days (Mandiant, part of Google Cloud). The median organization takes 43 days to patch one (Verizon DBIR 2026). A new free guide explains how autonomous AI agents are closing that gap, and what security leaders...
China-Aligned FamousSparrow Deploys SparroWocky Backdoor Across Latin America
The China-aligned state-sponsored threat actor known as FamousSparrow has been observed deploying a previously unreported backdoor called SparroWocky in attacks targeting multiple countries in Latin America since at least August 2025. "SparroWocky is a modular, C++...